“
CompTIA Security+ SY0-801 is projected to launch on November 17, 2026 (Source: CompTIA). However, you must check the confirmed date right before you book the exam. The old version SY0-701 retirement date (for the English version only) is on June 11, 2027, and for other languages (Japanese, Thai, Spanish, and Portuguese), the retirement date is August 13, 2027. The updated SY0-801 CompTIA Security+ V8 maintains the five-domain framework while adding specific AI security coverage.
”
Introduction
If you’re studying for CompTIA Security+, you may have heard about the upcoming SY0-801 exam. Perhaps you’ve already begun studying SY0-701, purchased a practice exam, or enrolled in a training program. You might be thinking if you should continue your preparations or wait for the next edition.
This is a valid issue. Nobody likes to spend months studying for an exam only to realize that the objectives have changed.
The good news is that you don’t necessarily have to start again. CompTIA Security+ V8 maintains the classic five-domain structure while upgrading the subjects to address modern-day cybersecurity threats. Understanding the CompTIA Security+ Sy0-801 release date 2026, SY0-701 retirement dates, and exam changes will help you select the best preparation method without wasting time or money.
This guide exactly assists you what you are looking for like SY0 801 release date, SY0-701 vs SY0-801 comparison, SY0-801 practice test, and much more.
Key Takeaways
“
- The SY0 801 release date is clearly mentioned, but not engraved in stone. CompTIA states “on or around” November 17, 2026, so check their page before booking.
- The English SY0-701 will be valid for almost seven months (June 11, 2027) after CompTIA Security+ V8 launches.
- The Japanese, Thai, Spanish, and Portuguese SY0-701 exam versions will be retired after nine months (August 13, 2027) after V8 version launches.
- Candidates who are already preparing for the SY0-701 exam may continue with the same study plans, as there are no major changes in the CompTIA Security+ V8 exam domains (Program Management drops from 20% to 14%, while General Security Concepts rises from 12% to 16%).
”
What is CompTIA Security+ SY0-801 Exam?
CompTIA Security+ SY0-801 exam is designed to validate major cybersecurity knowledge and practical study capabilities. It is currently the 8th version of the Security+ certification exam. The exam domains cover threat detection, vulnerability management, security architecture, and organizational security practices.
One significant change in the new version is the increased focus on AI-related cybersecurity issues. As companies implement AI tools, security experts must understand how these technologies might introduce vulnerabilities, expose data, and open up new ways for attackers to get into the system.
CompTIA claims the SY0 801 exam is ISO 17024 recognized by ANAB and requires two years of practical experience as a security administrator. Many learners gain confidence via practical labs and practice tests initially.
CompTIA Security+ SY0-801 Release Date: When Does It Launch?
The SY0 801 release date is on or around November 17, 2026 as per CompTIA official website. As it says, “on or around” that day, it means it can be shifted slightly. Therefore, you must visit the official website before you book the new version of the exam.
Here are important dates to remember:
| Milestone | Date | Current Status |
|---|---|---|
| SY0-701 (V7) Launch | November 7, 2023 | Live |
| SY0-801 (V8) Launch | November 17, 2026 (on or around) | Expected |
| SY0-701 Retires (English) | June 11, 2027 | Scheduled |
| SY0-701 Retires (Japanese, Portuguese, Spanish, Thai) | August 13, 2027 | Scheduled |
| SY0-801 Retirement | About 3 years after launch | Not Scheduled |
The variation between these dates is important. CompTIA lists the November 17, 2026 launch date as an expected date, and the SY0-701 retirement dates as scheduled retirement dates.
Until CompTIA provides SY0-801 scheduling, you can only book SY0-701. Before you pay for any exam, go to the CompTIA V8 page and double-Check the date.
SY0-701 Retirement Date: How Long Can You Still Test?
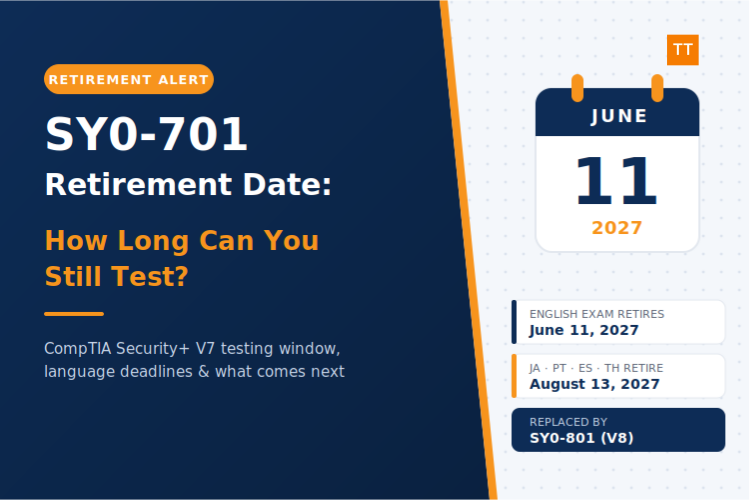
The English version of CompTIA Security+ SY0-701 exam is set to retire on June 11, 2027. The Japanese, Portuguese, Spanish, and Thai exam versions are set to be retired on August 13, 2027.
This indicates that applicants who speak English still have the opportunity to finish the current examination following the scheduled V8 release.
Nevertheless, do not combine exam retirement with the expiration of certification. If you successfully complete SY0-701 prior to its retirement, your Security+ certification will not be declared invalid upon the introduction of SY0-801 by CompTIA.
Always check CompTIA’s Security+ V7 website before booking a test, especially if you are approaching the retirement date.
SY0-701 vs SY0-801: What Are the Major Differences?
CompTIA Security+ V8 maintains five domains while altering their titles, proportions, and focus areas. The most visible upgrade is the increased focus on AI security and current cybersecurity threats.
Here is a SY0-701 vs SY0-801 exam comparison you must know before you book the exam:
| Feature | SY0-701 | SY0-801 |
|---|---|---|
| Exam Version | V7 | V8 |
| Launch Date | November 7, 2023 | ~November 17, 2026 |
| Retirement | English: June 11, 2027 Other languages: August 13, 2027 |
Estimated 3 years after launch |
| Security Domains | 5 | 5 |
| Domain Weightings | ||
| General Security Concepts | 12% | 16% |
| Threats and Vulnerabilities* | 22% | 24% |
| Security Architecture | 18% | 19% |
| Security Operations | 28% | 27% |
| Security Program Management and Oversight | 20% | 14% |
| Recommended Experience | Network+ certification and two years of experience in a security or systems administration position | Security administrator with two years of practical experience |
📌 Note
Threats, Vulnerabilities, and Attacks is the new name for the second domain in the Security+ V8 exam. The fundamental framework remains easily recognizable, so current expertise in networking, access control, cryptography, vulnerability management, and incident response is applicable to both versions.
Two numbers require your attention. First, Security Operations and Threats account for 51% of V8; therefore, those two categories account for about half of your total score. Second, Program Management is down six points. But it’s not dead. Don’t skip risk assessments, audits or policies.
For candidates, this means that just recycling an old study plan without first reviewing the new goals is not an effective preparation technique.
Also Read: CompTIA Security+ Certification Study Plan, Jobs & Salary Guide
SY0-801 Exam Format
The SY0-801 test contains a maximum of 90 questions, lasts 90 minutes, includes both multiple-choice and performance-based questions, and requires a score of 750 on a scale of 100 to 900 to pass. CompTIA specifies English as the only available language for now.
Performance-based questions are hands-on assignments in which you act out a scenario rather than selecting from four options. Practice them ahead of time to avoid surprises on exam day.
A SY0-701 voucher costs between $425 and $439 in the United States, according to pricing guidelines for 2026. Therefore, it is expected that the new SY0-801 exam cost will be around $439 in the US. However, you must double-check when booking for the exam as per your region.
CompTIA also suggests appropriate hands-on security expertise. Its suggested background includes expertise as a security administrator; however, this is not the same as a rigorous test prerequisite.
When SY0-801 becomes available, candidates should contact CompTIA to confirm the final test structure and schedule information.
What Is Changing in CompTIA Security+ V8 (SY0-801)?
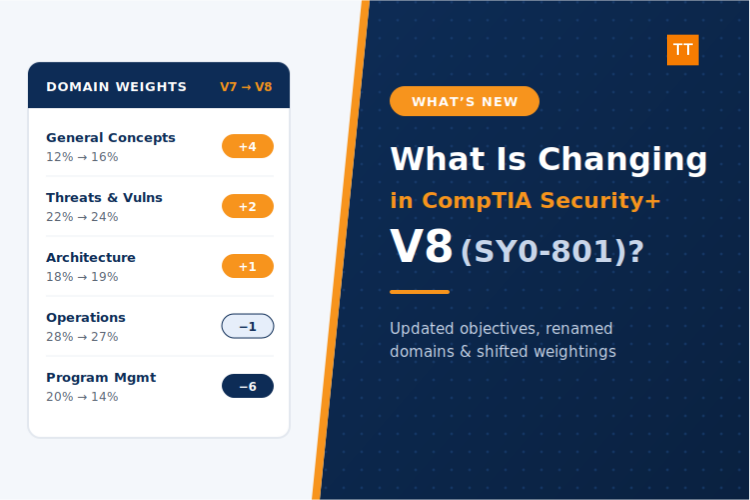
The most significant change is artificial intelligence. Security+ V8 establishes a defined target for AI security threats, which include risks to AI systems, models, prompts, privacy, and data disclosure. These changes reflect the problems that cybersecurity teams confront in today’s information technology settings.
1. Greater Focus on AI Security
SY0-801 focuses more on AI security. Candidates have to understand how AI systems might bring security vulnerabilities and how attackers can exploit them.
Important areas are:
- Prompt injection attacks
- AI Model Poisoning
- AI-related data exposure
- Privacy and information security concerns
- Jailbreaking and attempts to bypass protections
- AI model and app security problems
Consider an employee using an AI assistant to process secret company data. If the system is not properly secured, sensitive information may be exposed via its prompts or outputs.
Security experts must be aware of these threats and have the right security measures in place.
2. Updated Cybersecurity Threats and Attack Techniques
Cyberattacks are evolving, with many attackers discovering new methods to employ existing strategies. Phishing, impersonation, and malware remain big issues, but the technologies used to carry out these assaults have advanced. Topics covered in Security+ SY0-801 V8 include deepfake impersonation, QR-code phishing, fileless malware, and the exploitation of legitimate system utilities.
These strategies are essential because attackers do not always have to breach a firewall. They may deceive personnel, steal passwords, or gain access through trusted programs.
3. Modern Security Architecture
Security architecture remains a critical component of the updated CompTIA Security+ exam. Candidates should be aware of how businesses secure the standard infrastructure, cloud platforms, remote users and networked systems.
Important areas include the following:
- Zero Trust Architecture
- Cloud Security
- Hybrid Infrastructure
- Security Service Edge (SSE)
- Identity and Access Management
- Least privilege
- Data Protection and Recovery
Zero Trust is especially essential since it demands that enterprises authenticate access rather than immediately trusting people or devices just because they connect to an internal network.
4. Updated Security Operations
Security Operations continues to be the largest exam domain in SY0-801, accounting for 27% of the total.
It focuses on the day-to-day tasks of system protection, suspicious activity monitoring, vulnerability management, and security incident response.
For example, if a security monitoring tool identifies suspicious login activity, a security analyst may need to study system logs to identify the source, determine whether an account has been hacked, and take necessary action.
The expanded objectives include covering current security technology, automation, and AI-powered security operations.
5. Changes in Security Program Management and Oversight
The CompTIA Security+ V8 exam still includes Security Program Management and Oversight; however, its weighting is lowered from 20% to 14%.
This area addresses organizational security duties such as risk management, governance, compliance, policies, audits, and security awareness.
Despite its low ratio, candidates shouldn’t ignore it. Understanding how an organization handles security threats is critical for certification tests and professional cybersecurity jobs.
Also Read: Can You Get a Cybersecurity Job With Only CompTIA Security+ in 2026
Updated SY0-801 Exam Domains and Weightings
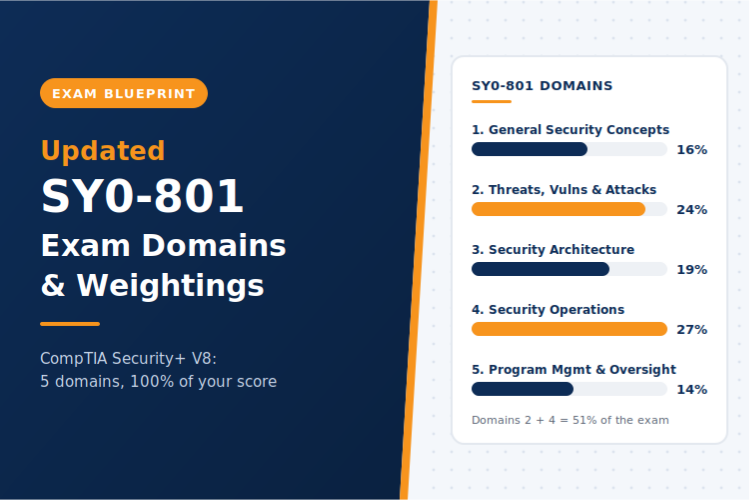
Here are the updated SY0-801 exam domains with their weightings as per the official CompTIA Security+ page:
1. General Security Concepts (16%)
- Compare and contrast the following types of security controls: Understand how layered security measures safeguard systems and data.
- Demonstrate the security impact of change management methods: You can see how planning, testing, approvals and documentation all lead to secure settings.
- Explain how important it is to use proper cryptographic solutions: Implement encryption, certificates, hashing, digital signatures, and key management procedures.
2. Threats, Vulnerabilities, and Attacks (24%)
- Compare and contrast typical threat actors and motivations: Understand who is behind attacks and why organizations are targeted.
- Explain common attack vectors and attack surfaces:Determine how attackers target users, systems, apps, networks, cloud resources, and supply chains.
- Analyze indications of malevolent behavior: Recognize symptoms of malware, social engineering, credential assaults, and other security concerns.
- Examine common weaknesses and related risks: Evaluate vulnerabilities and contribute to determining mitigation priorities.
- Explain the security threats related to artificial intelligence (AI): Identify the hazards associated with AI systems, models, prompts, privacy, and data exposure.
3. Security Architecture (19%)
- Compare and contrast the security implications of various architectural models:Understand the security implications for cloud, hybrid, on-premises, and operational technology settings.
- Use security principles to protect enterprise infrastructure: Ensure safe system design, access controls, segmentation, and connectivity.
- Understand the concepts of data protection: Protect sensitive data throughout its lifecycle.
- Discuss the significance of resilience and recovery in security frameworks: Backups, redundancy, recovery planning and testing are all means to achieve continuity.
4. Security Operations (27%)
- Use typical security approaches for computing resources: Help protect endpoints, networks, applications, and data.
- Explain asset management concepts and procedures: Manage hardware, software, and data assets over their entire lifecycle.
- Explain security monitoring and alerting ideas: Use logs, alerts, dashboards, and security technologies to detect potential risks.
- Manage identity and access controls: This includes authentication, authorization, clustering, and privileged access management.
- Explain the value of automation and orchestration in security operations: Increase efficiency with automation, integrations, and AI-assisted workflows.
- Implement incident response activities: Assist with preparation, detection, containment, recovery, and lessons learned.
- Use data sources to support your investigations: Analyze evidence and data security during an inquiry.
5. Security Program Management and Oversight (14%)
- Define the components of an effective security governance program: Apply rules, standards, processes, and security guidelines.
- Manage security risk management procedures and principles: Assessment, communication, and management of organizational risk.
- Explain third-party risk management ideas: Assess and monitor vendor and partner security threats.
- Support security compliance and privacy considerations: Meet regulatory, legal, compliance, and privacy standards.
- Compare and contrast audits and assessments: Participate in audits, reviews, tests, and evaluations.
- Encourage security awareness behaviors: Help to improve organizational security through education and awareness.
Should You Take SY0-701 Now or Wait for SY0-801?
Your decision should be based on how much preparation you’ve done and when you want to take the exam. If you are already studying SY0-701, it is usually a good idea to continue. Prepare for SY0-801 if you are beginning from scratch and want to test after its retirement.
| Your Situation | Better Choice |
|---|---|
| Already studying and nearly ready | SY0-701 |
| Job or promotion needs the cert soon | SY0-701 |
| Starting from zero, testing after mid-2027 | SY0-801 |
| Testing in Japanese, Portuguese, Spanish, or Thai | SY0-701 V8 is English only so far |
| Want AI security on your resume | SY0-801 |
Here’s a basic rule. Count backward from June 11, 2027, allowing at least a month for a rescheduling or retake. SY0-701 is appropriate if your honest study plan falls within that time frame. If not, V8 is the better option.
Two precautions. Waiting just because something is new might cost you months of professional time. If you pick SY0-701, make your reservation as soon as possible to avoid missing the deadline due to a busy schedule. Always ask your company or school whether they demand a particular version.
A Simple Study Plan for Either Exam
A six-week schedule works well for many students who can study 8 to 10 hours each week, and the same plan applies to both SY0-701 and SY0-801.
- Weeks 1 and 2:Cover general security concepts and threats.
- Week 3: Study Security Architecture
- Week 4: Prepare for security operations, your core domain.
- Week 5: Program Management, including AI subjects if you are pursuing V8.
- Week 6: Timed practice test from Troytec using a test engine or PDF versionand a review of weaknesses with the Troytec AI assistant.
FAQs (Frequently Asked Questions)
Conclusion
The recent release of CompTIA Security+ SY0-801 includes significant upgrades to the certification, notably in AI security, current cyberattacks, and security operations. However, the shift does not imply that applicants who are already preparing for SY0-701 must quit their efforts.
If you’ve already invested time preparing for SY0-701, you can finish it and take the test before it expires. There is no need to upgrade to the new version and begin learning over again. If you’re starting, choose SY0-801 based on your preparation timetable and exam date.